
PayPal
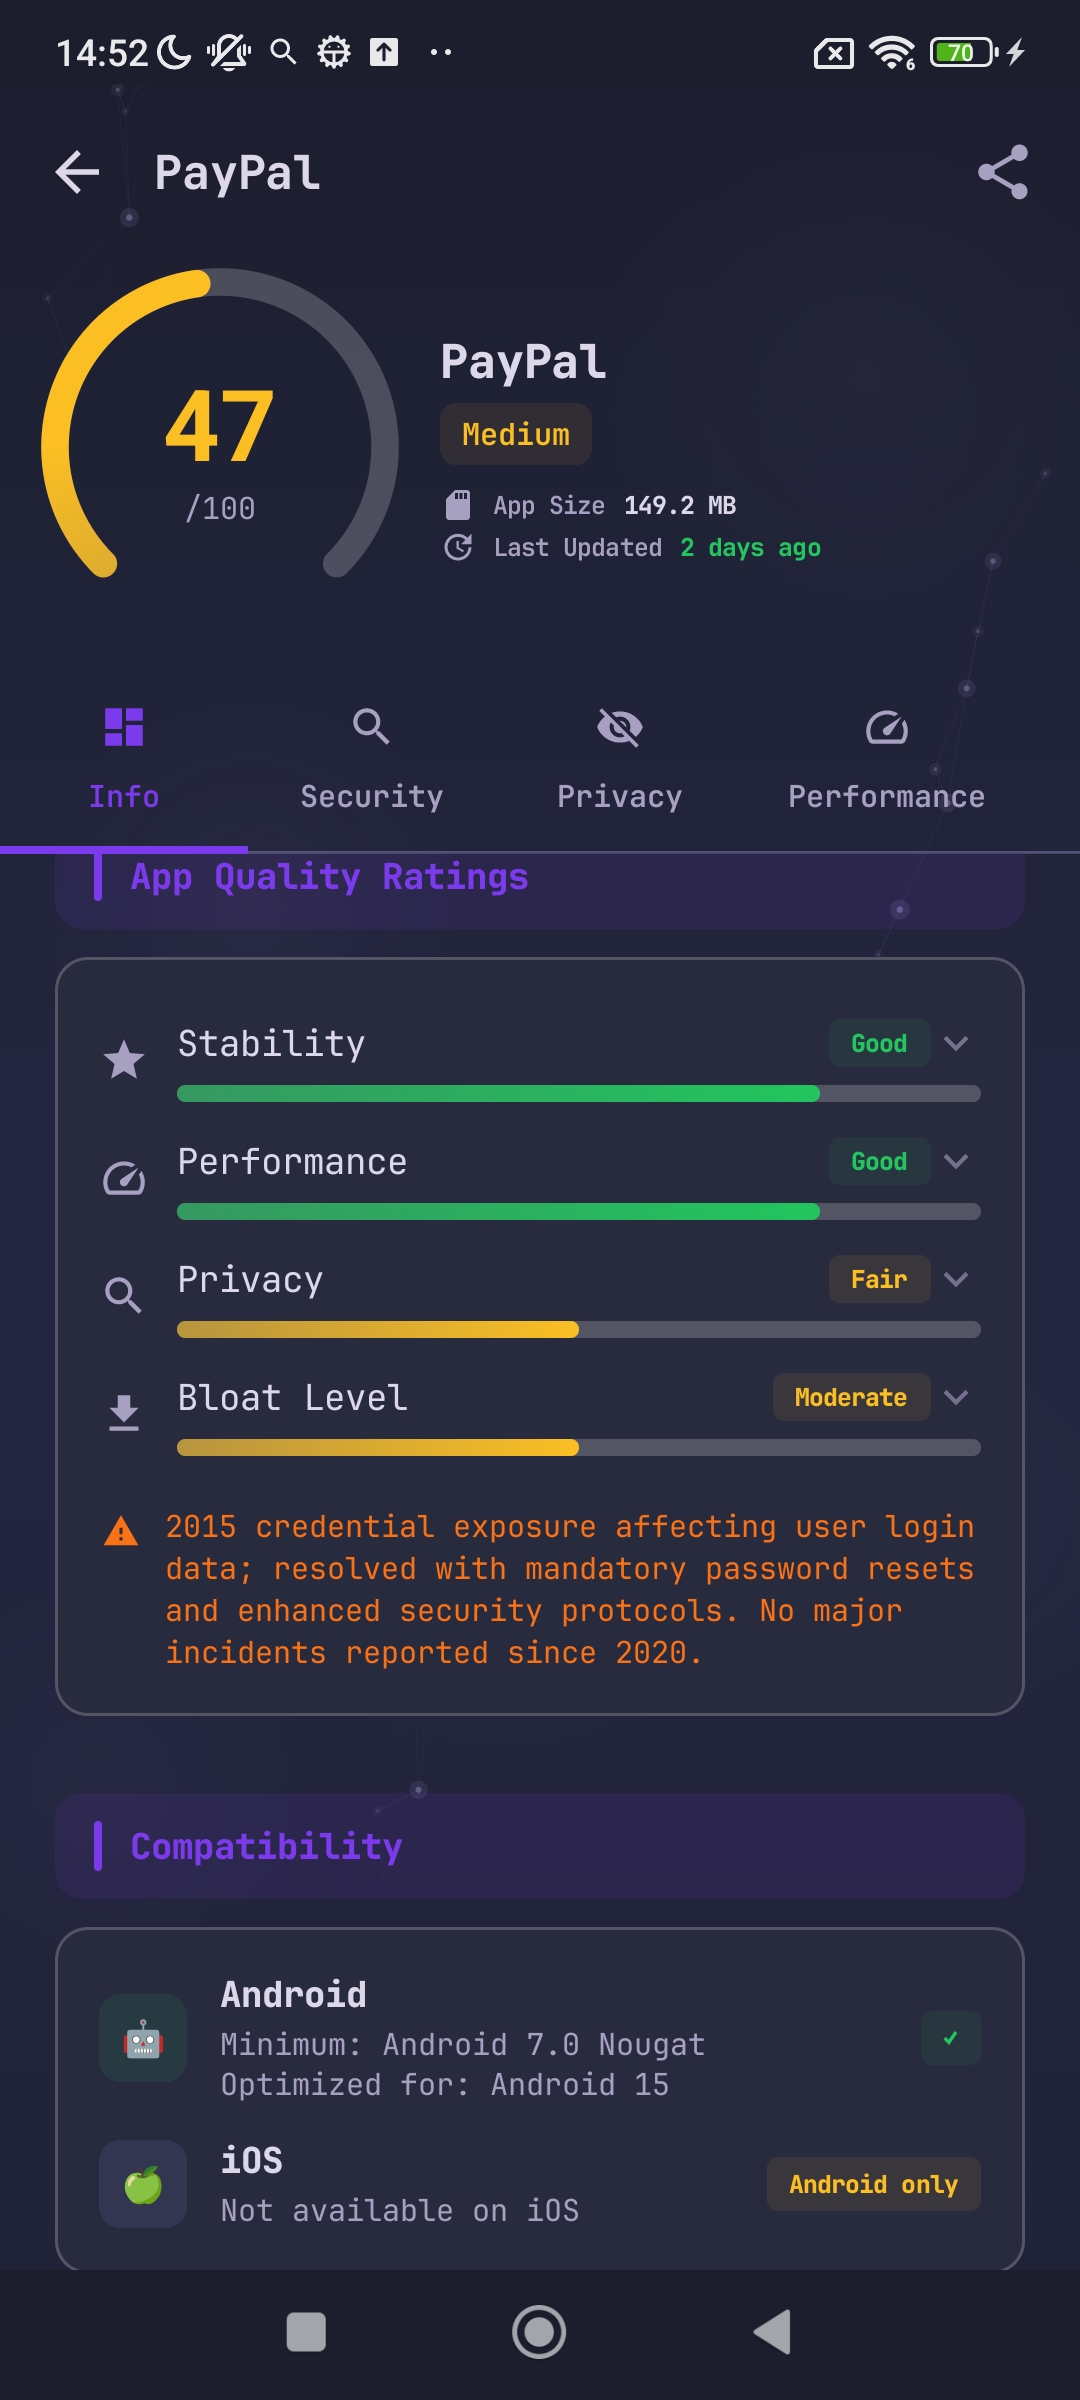
PayPal is a legitimate, well-established financial app with strong encryption and fraud protection, but it collects substantial data across 13 verified trackers (analytics, advertising, attribution, and payment processors) and requests 6 dangerous permissions including location, contacts, camera, and microphone. While these permissions may support features like in-store payments and identity verification, the combination of broad data collection and third-party ad networks elevates privacy risk to MEDIUM despite PayPal's reputation.
Regulierung & Recht
2015 credential exposure affecting user login data; resolved with mandatory password resets and enhanced security protocols. No major incidents reported since 2020.
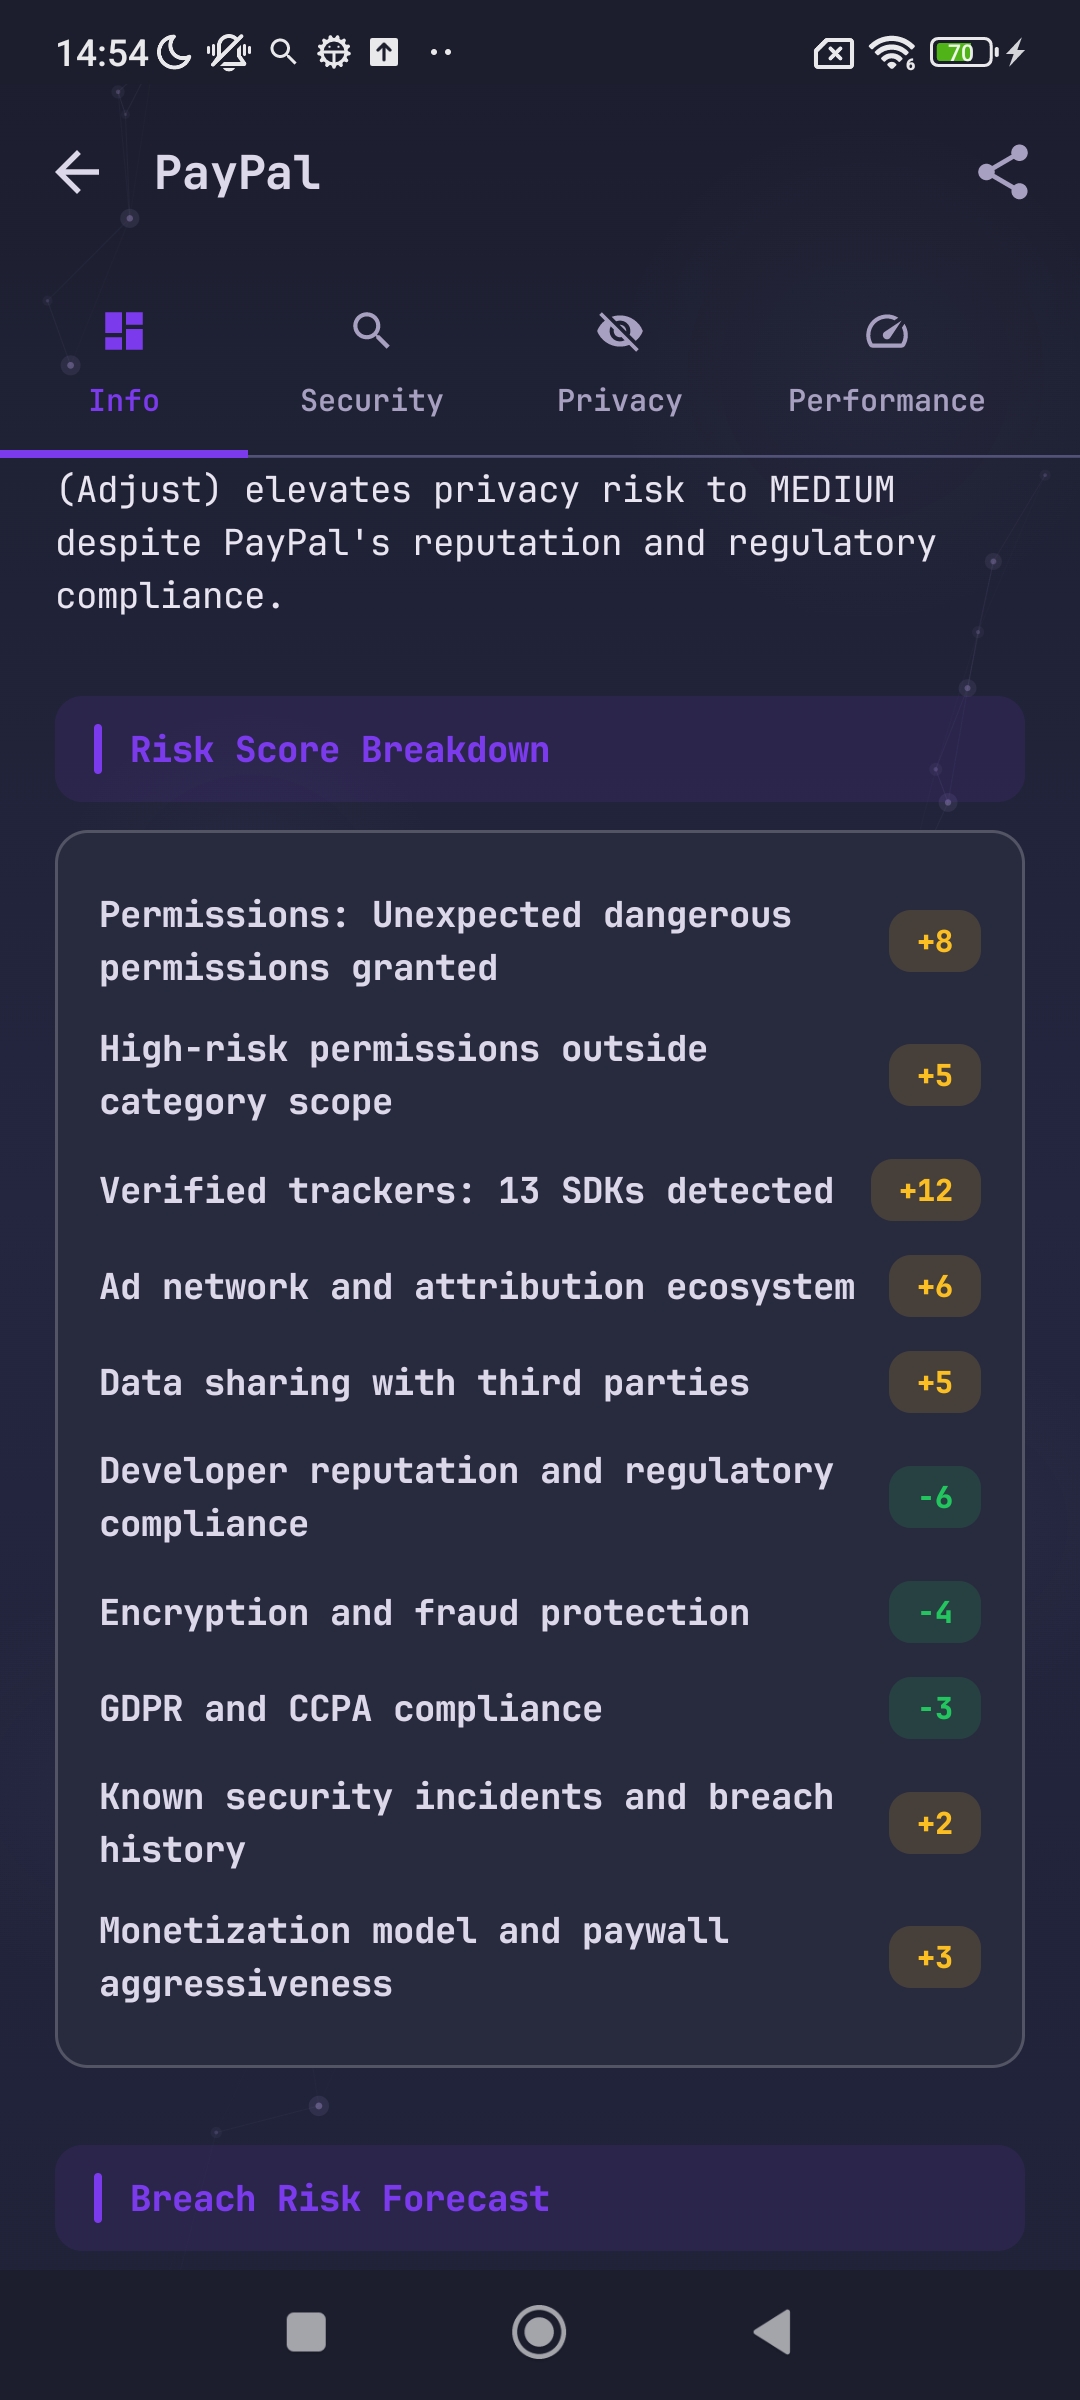
So kommen wir auf 47.
Location, camera, contacts, microphone - not all clearly justified for payments
RECORD_AUDIO and CAMERA together create exfiltration risk
4 analytics, 2 ad networks, 1 attribution, 1 crash reporter
Google AdMob, Meta SDK, Adjust enable behavioral profiling
Transaction and behavioral data shared with multiple vendors
Publicly traded, heavily regulated (NMLS, NY DFS), strong compliance
TLS, biometric auth, tokenized payments, fraud detection
2015 credential exposure affecting login data
Versteckt im Code.
Was sie verlangt.
Microphone on a payments app - questionable necessity
For check deposits and QR scanning
For contact-based payments
Device state monitoring and fingerprinting
Precise GPS for in-store payment features
Aus dem Scan.

Weiter lesen.
What trackers are actually hiding in your apps
We scanned 32 of the most-installed Android apps and counted every embedded tracker SDK. The average app hides 5 tracker...
Why does this app need microphone permission?
Why do apps request microphone, location, or contacts access they don't need? A field guide to Android permission creep ...
Ähnliche Risikoprofile.
Scanne PayPal selbst.
Hol dir den vollständigen Report auf deinem Gerät - mit Echtzeit-DEX-Analyse, Berechtigungs-Audit und Breach-Monitoring. Kostenlos, ohne Konto.